Tags and secrets
Two kinds of placeholder work inside text fields: {tag} for a value from a wire, and {{secret.NAME}} for a stored key.
{tag}: a value from a wire
Section titled “{tag}: a value from a wire”In a Template, type a word in braces and it becomes an input socket:
Reply to {customer} about this ticket in two sentences:
{ticket}
This Template grows customer and ticket sockets. Wire into them, and when the Template runs each tag is replaced by the wired value. Dropping a wire on the Template’s empty socket adds one named after the source node; type that name in braces where the value should go.
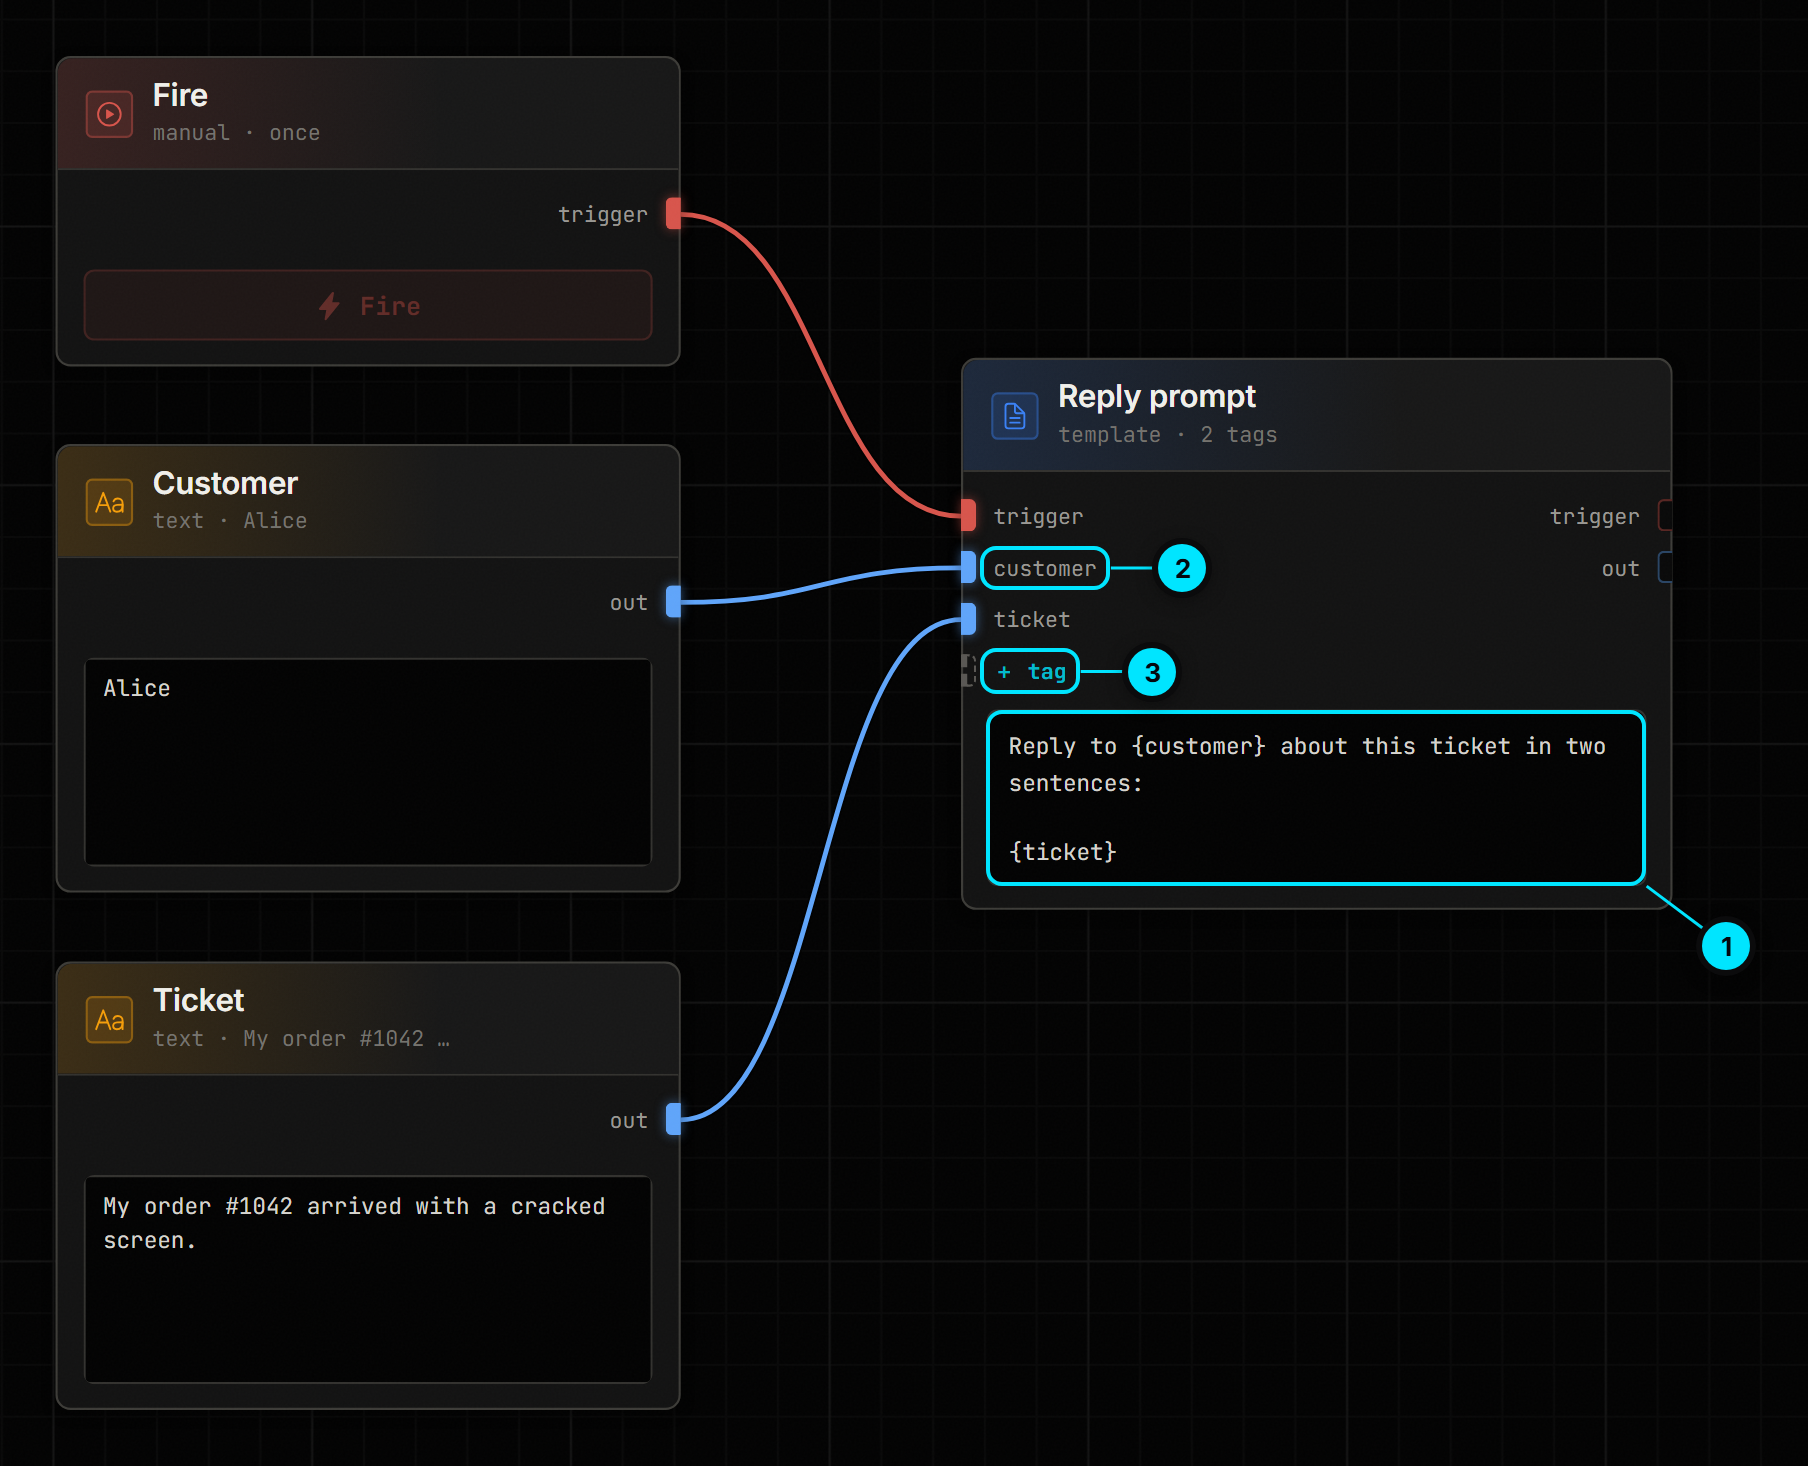
- The text, with
{customer}and{ticket}in braces. - The
customersocket that{customer}grew. Text nodes named Customer and Ticket feed the two sockets. - The empty
+ tagsocket: drop a wire here to add a socket named after the node it comes from.
The same tags work in the fields of HTTP Request (URL, headers, query, body), DB, KV and Vectors: wire into the node’s tag socket and use its name in the field, for example a URL of https://api.example.com/users/{user_id}.
Two details worth knowing:
- A wired tag whose value is empty becomes empty text. A tag with no wire at all stays as written, so a typo shows up in the output instead of vanishing.
- In a DB node’s SQL, a tag is never pasted into the statement: it is bound as a value.
SELECT * FROM notes WHERE id = {id}is safe even whenidcomes from a webhook.
{{secret.NAME}}: a key that stays out of the graph
Section titled “{{secret.NAME}}: a key that stays out of the graph”Add a secret in Settings › Secrets: a name in capitals, digits and underscores (MY_API_KEY) and its value. Then use it in any field that takes secrets, such as an HTTP Request header:
Authorization: Bearer {{secret.MY_API_KEY}}The value is filled in when the node runs. The graph file only holds the token, so a graph that uses secrets is safe to share.
- A token also reads the provider keys Boltjar knows (
XAI_API_KEY,ANTHROPIC_API_KEY,GOOGLE_API_KEY,OPENAI_API_KEY,FISH_API_KEY,ELEVENLABS_API_KEY), from Settings › AI Providers or from.env. It never reads any other environment variable, so a graph from someone else cannot ask for yourAWS_SECRET_ACCESS_KEY. - A graph that uses a secret nobody defined does not turn On, and the problems list names the secret.
- Live values in the editor show a known secret (8 characters or longer) as its token, not its value.
Secrets you add in the editor are stored in user/data/secrets.json, in plain text, like .env. Both are ignored by git. Security has the details.
A key typed straight into a field, without a token, is saved in the graph file and its snapshots. Use a secret instead.